Self-hosted log management and threat detection for classified, air-gapped, and
regulated networks. Collect, enrich, detect, and respond — entirely inside your
environment. No telemetry.
Drag the ring or use ← → to turn it; click a window to explore.
FIPS 140-3
DISA STIG
CIS Level 1
OCSF v1.3
Air-gap capable
What logrok does
From raw log to resolved incident
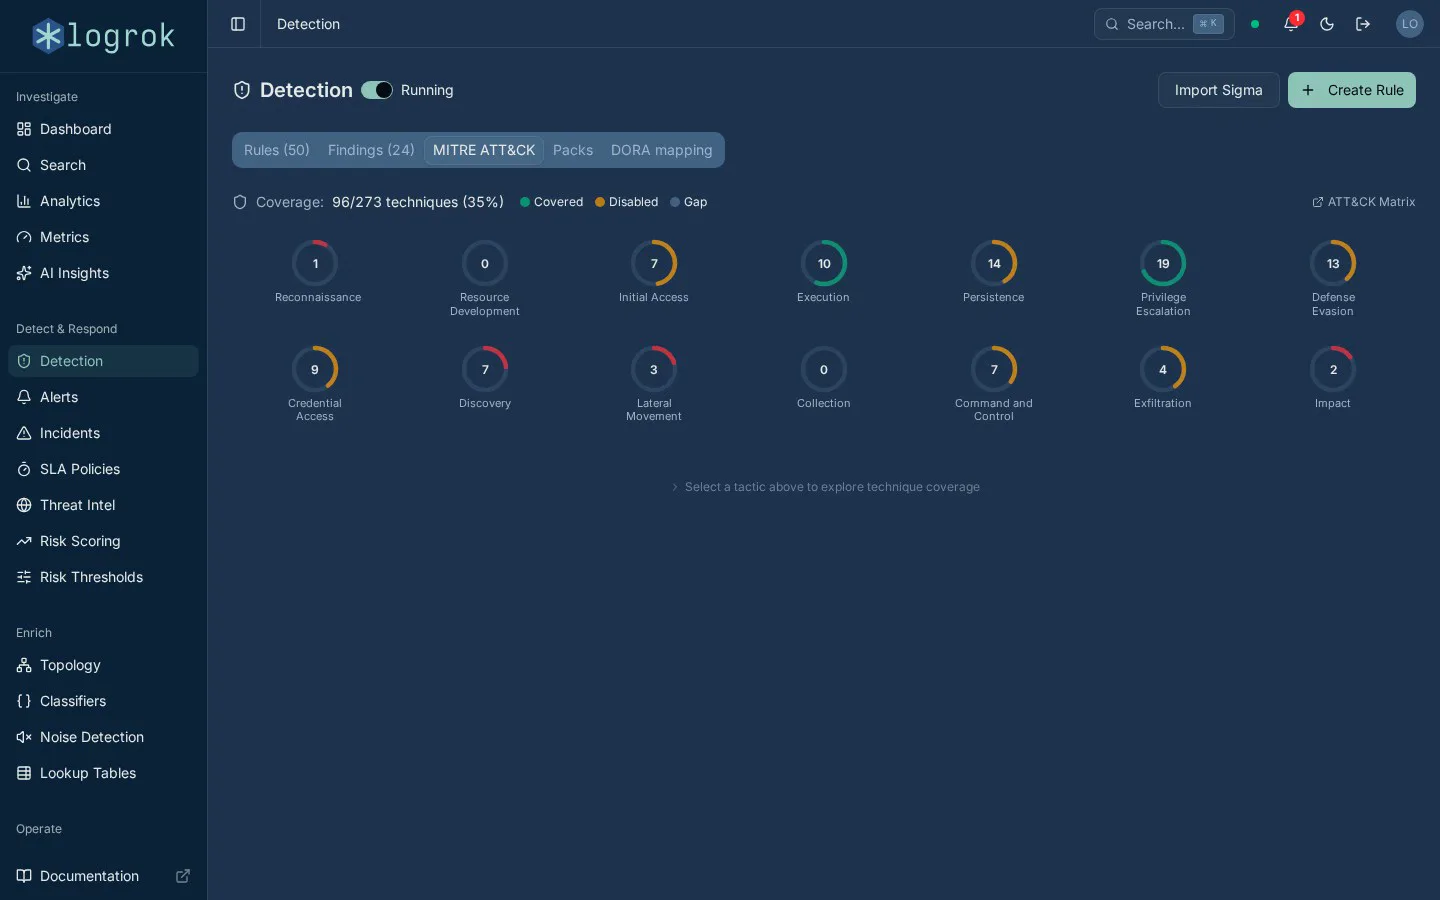
Follow one event through logrok. Every window below is the real product, captured from a release appliance.
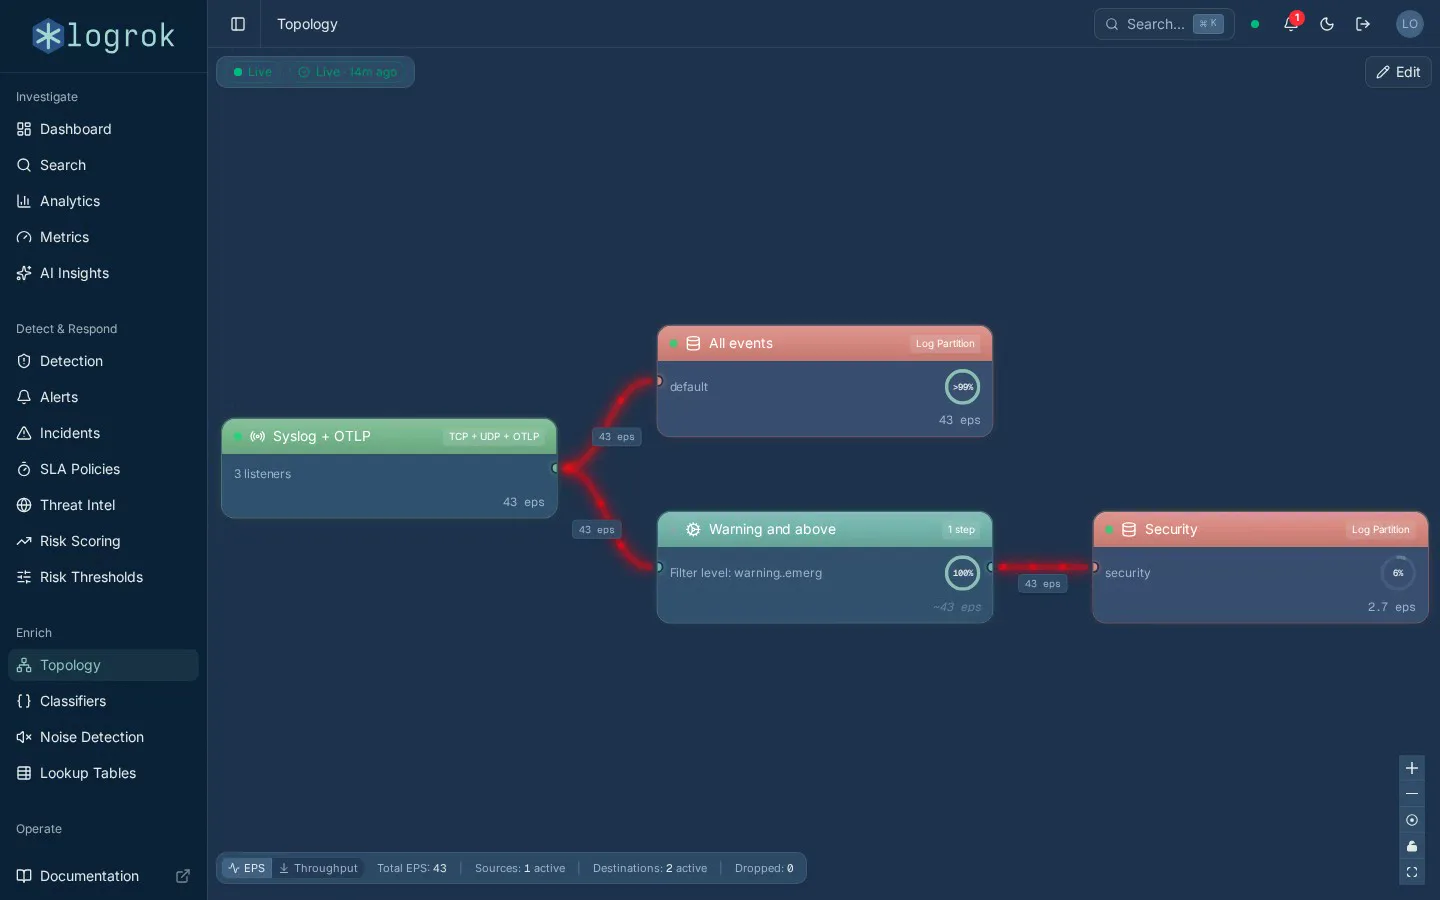
Collect & route
Every source, one live pipeline
Syslog over TCP, UDP, TLS and RELP, OTLP/gRPC, Kafka, Azure Event Hub, HTTP webhooks and files, drawn as a topology you can read at a glance, with LUnA agents at the edge.
NewSNMP traps from network devices and appliances: SNMPv3, v2c and v1
NewEvery edge labeled with its own measured rate
Each change goes live as a versioned deploy, with rollback
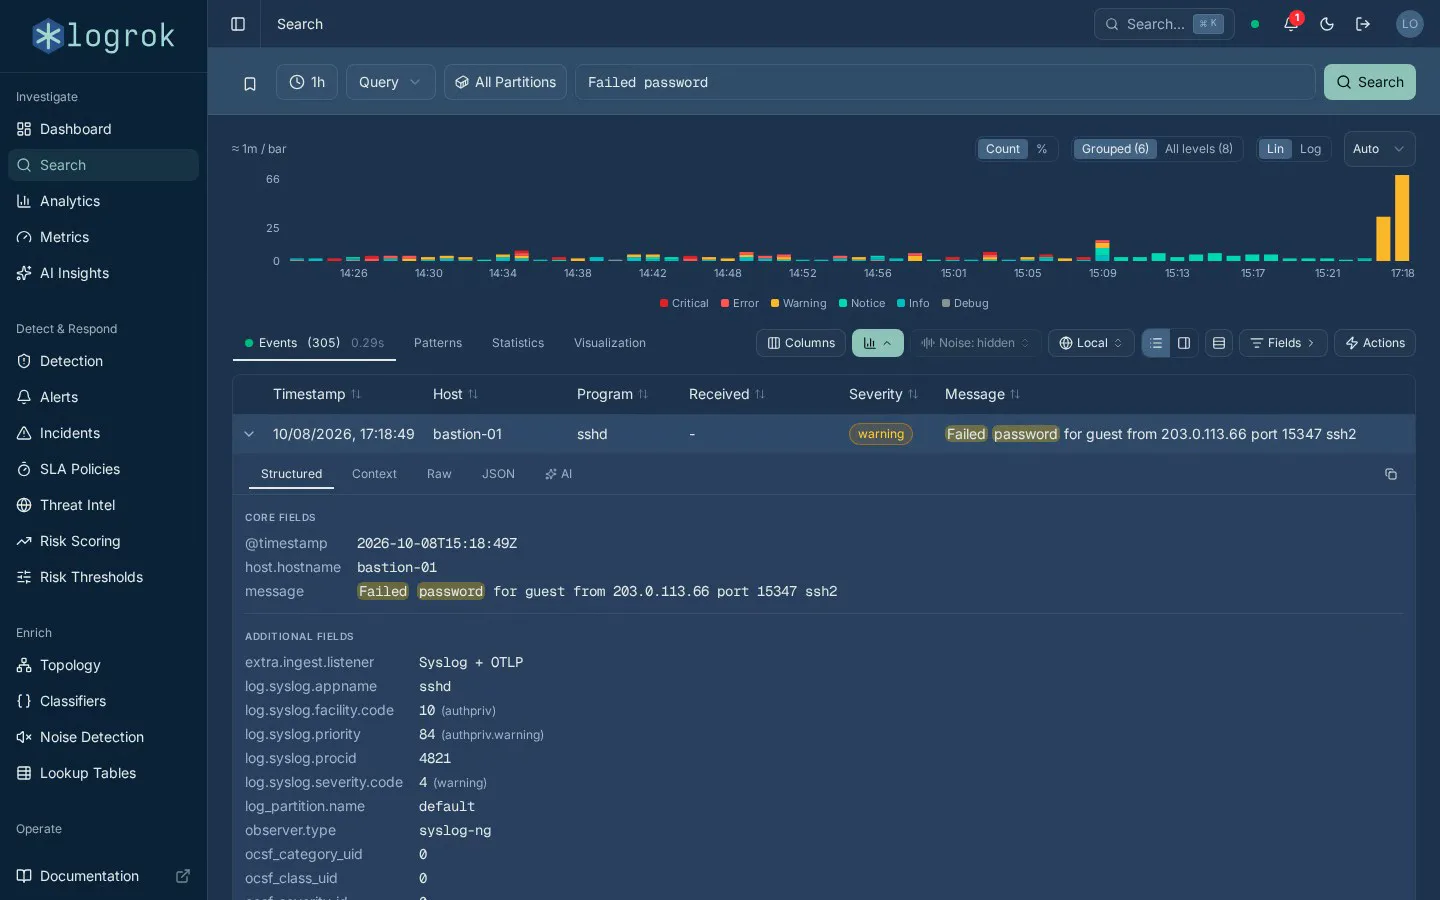
Plain text, regular expressions, field queries, SQL filters and natural-language AI over the same log store. Switch any result to Patterns, Statistics or a chart, and ask what stands out in a spike.
NewFind any value a field holds, not only the top 200
NewFilter noise per template, kept in your saved views
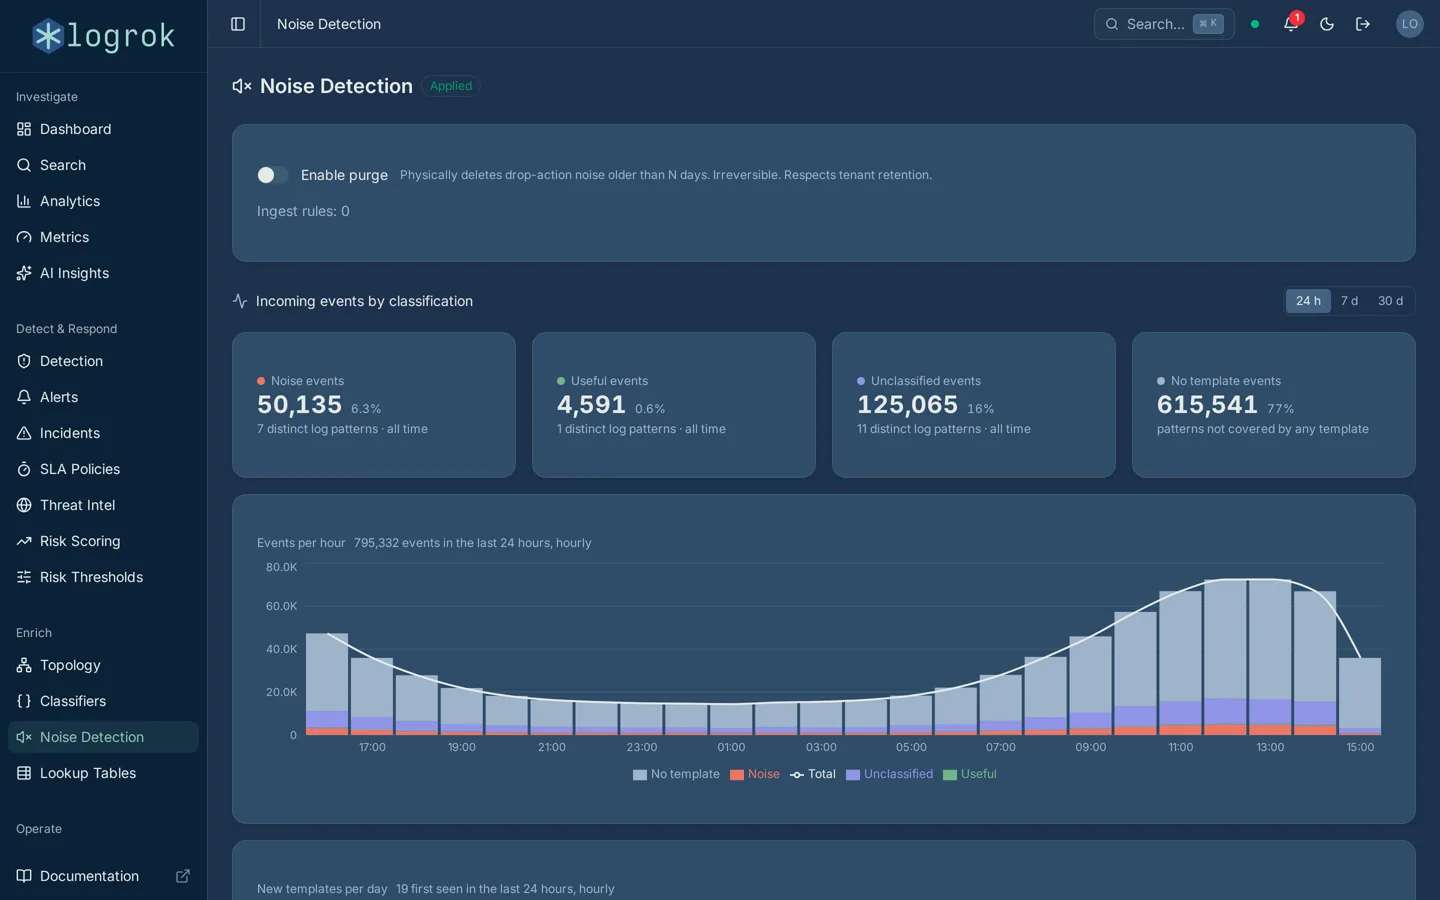
logrok extracts and classifies repetitive patterns automatically. For each one you choose to monitor, tag, route or drop it, at ingest or on the sending host, so a dropped event never crosses the network.
One fingerprint lookup per event on the host, however many templates
NewClassifiers store what they recognize as searchable fields, with 28 ready-made templates
NewExport your noise decisions and import them on another installation
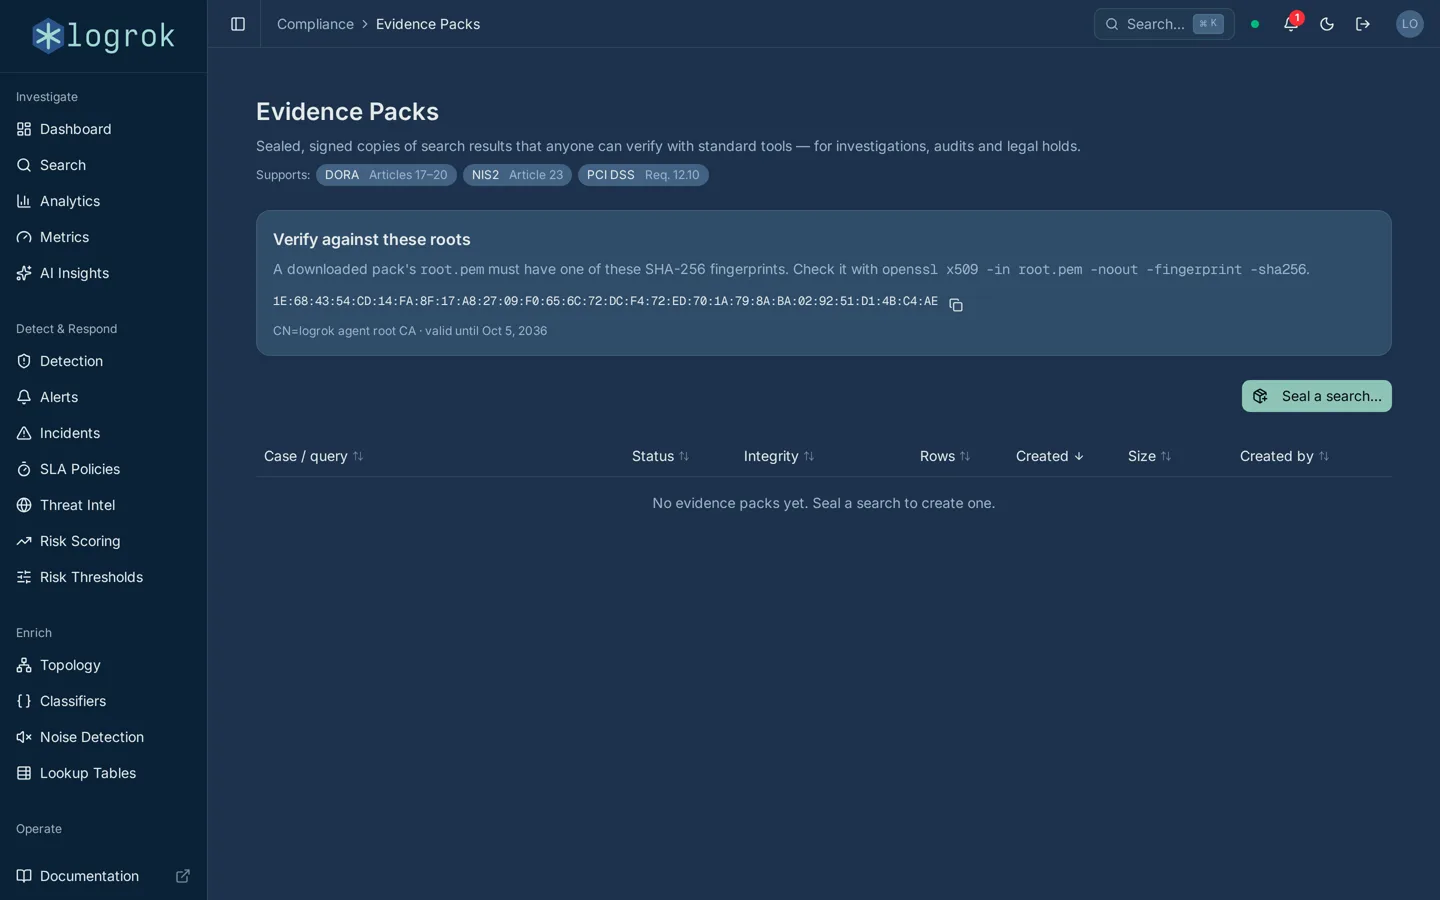
Seal a search into a signed, encrypted evidence pack that anyone can verify with OpenSSL, sha256sum and zstd, no logrok needed. Licensed DORA, NIS2 and PCI DSS packs add framework-mapped evidence.
LUnA, the logrok universal agent, is one static binary for Windows, Linux and macOS. Enroll, configure, upgrade and monitor every agent from one Agents page, with per-agent mTLS.
NewDelivery latency and FIPS posture for every agent
NewOperator-signed configurations
NewA lost-events breakdown that says why, with a remedy for each cause